NEXIS INVOLVE 2026: Ideas, Experiences and a Community Shaping Identity Security
22 Sep 2026
What happens when the people defining identity governance strategies meet the people putting them into practice every day?
For two days in September, we had the chance to find out. And this year, that exchange took place in English for the first time, with guests from seven nations in the room.
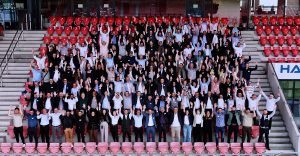
On September 9 and 10, the NEXIS community came together at the Jahnstadion in Regensburg for the largest NEXIS INVOLVE yet. Customers, partners, IAM and GRC professionals and security experts joined us to share experiences, challenge ideas and take an honest look at where identity security is heading.
The agenda covered a lot of ground: AI agents and non-human identities, role engineering, application onboarding, continuous compliance, GRC and the growing connection between all of these areas.
And while every organization brought its own perspective, many of the questions raised in one session returned in another. That made for two days with plenty to discuss.
Setting the stage for what comes next
Dr. Heiko Klarl opened INVOLVE with a look at how the identity landscape is changing and what that means for Nexis and the NEXIS Platform.
Traditional IAM is no longer the whole picture. Human identities now share the landscape with machine identities, workloads and AI agents. Cloud environments add further complexity, while access itself is becoming more dynamic and contextual.
Yet behind all that change are some remarkably persistent questions: Who or what has access? Why? Who is responsible for it? What risk does it create? And can we demonstrate that our controls are actually working?
Dr. Michael Kunz and Dr. Matthias Hummer then took that perspective into the NEXIS Platform itself and shared what comes next.
Their roadmap provided a closer look at developments around identity visibility, evidence collection, access reviews, third-party governance and the governance of AI agents. NICO, the NEXIS Intelligent Copilot, showed another side of that evolution by making complex governance information easier to access and work with.
Another focus was the move beyond purely static access models. Roles remain important, but attributes, relationships and context increasingly matter as well. The challenge is to make access more dynamic without making governance impossible to understand.
Together, the Nexis sessions set the stage for much of what followed. The questions raised here were not distant future scenarios. Many of them are already part of the day-to-day reality of the organizations that took the stage next.
Different industries, different challenges – and a lot in common
The customer presentations brought those questions into practice.
A perspective from a global automotive company showed how identity governance can become part of a much broader digital governance landscape.
Rather than looking at IAM in isolation, the organization is working towards connecting identity information with areas such as enterprise architecture and data governance. A central idea is to move beyond documenting what should happen and towards continuously understanding whether governance requirements are actually reflected in the environment.
As IT landscapes become more interconnected – and AI, OT and machine identities become part of the same picture – that connection between policies and reality becomes increasingly important.
When a pattern is not yet a role
Oliver Schluga from Erste Group approached governance from a different angle: the quality of roles.
Role mining can identify patterns in existing access data. But a pattern alone does not explain why access exists. Employees with similar organizational attributes may still legitimately require different permissions, while HR information alone may not provide enough context to design a meaningful business role.
Erste Group therefore looks at role design together with business context, attributes and Segregation of Duties. Analytics can reveal structure in the data, but the business still has to determine what that structure actually means.
Giving AI access to IAM – carefully
FI-TS brought AI directly into the IAM environment.
Operating in a highly regulated setting, the company has built an internal AI environment and is exploring how the Model Context Protocol, MCP, can connect it with trusted information from NEXIS.
This makes it possible to interact with identity information through natural language, for example when asking about users, roles or organizational structures.
But making IAM data easier to access also raises new governance questions. Which identity does an AI service use? Which information may it retrieve? How current is that information? And how do we deal with an answer that sounds convincing but is wrong?
AI can simplify the interaction with IAM. It does not remove the need to govern it.
Starting risk management with the business
Anton Rohr from SEFE moved the conversation from IAM into GRC.
At SEFE, information security risk management starts with the business process. The organization first looks at which processes and information are critical and which systems support them. From there, protection requirements can be transferred to the relevant assets, risks can be assessed and measures can be defined and tracked.
For a critical infrastructure organization operating across different entities and regulatory environments, keeping those relationships connected is essential. The GRC capabilities of NEXIS provide a common structure for linking business criticality, assets, risks, controls and measures – and for making that information available when it is needed for reporting or an audit.
Turning one IAM vision into a repeatable process
Wolfgang Zwerch and Timo Evers from Munich Re showed what identity governance looks like at scale.
As Munich Re and ERGO bring historically separate IAM environments closer together, one of the major challenges is integrating a large number of applications into a common governance model. Their answer is a standardized onboarding process: applications move through predefined waves, authorization concepts follow a common structure in NEXIS, and standard connectors are used wherever possible.
With hundreds of applications to onboard, every integration cannot become its own IAM project. Clear standards, responsibilities and timelines are what turn a target architecture into something that can actually be delivered.
A legal perspective on AI and accountability
Technology was only one side of the AI discussion at INVOLVE.
Patrick Schwarzbart from Lupp + Partner brought the legal perspective, looking at the EU AI Act and its interaction with established requirements around data protection, security and accountability.
AI agents make some familiar governance questions harder. Who is responsible when an AI system acts? What data may it use? Which obligations fall on the provider and which on the organization deploying it? And what happens when AI becomes part of processes involving sensitive identity information?
For the IAM community, this creates an important intersection: the more autonomy organizations give AI systems, the more relevant questions of ownership, controlled access and accountability become.
Partner perspectives: making governance work in practice
Our partners KOGIT and SonicBee brought two hands-on perspectives to the stage.
Building roles that last
Dr. Sven Hübner and Florian Frank from KOGIT shared their experience of moving from a complex authorization landscape towards sustainable role governance, including the interaction between SailPoint IdentityIQ and NEXIS.
Their session showed that role mining is only one part of the journey. Reliable data, clear ownership and a well-defined lifecycle are just as important if roles are meant to remain useful after the initial project has ended.
Putting identity visibility into practice
Timo Copp from SonicBee and Florian Hasibether from LINZ AG showed how NEXIS is being used across a growing number of operational IAM use cases at LINZ AG.
Their examples ranged from business roles and recertification to provisioning and server permission analytics. One particularly tangible question was how to determine who can actually access a server when permissions are spread across different systems, local accounts and groups.
The session also came with a very practical lesson from the implementation journey: understand your data, test properly and solve problems at their source before analytics becomes part of operational IAM processes.
Panel Discussion: what comes next for identity security?
The panel discussion brought several themes from the previous sessions together and looked further ahead.
AI agents and non-human identities were a major part of the conversation. As these identities become capable of taking increasingly independent actions, familiar IAM questions take on new meaning: Who owns an AI agent? What happens when its sponsor leaves? Which permissions should it have, and when does a human need to remain in the loop?
The discussion also touched on more dynamic and context-aware access models and the challenge of keeping them understandable and auditable.
There were no simple answers – and that was exactly the point. The panel offered a glimpse into some of the questions the identity security community will be working through in the years ahead.
Going deeper in the breakout sessions
INVOLVE is deliberately not only a main-stage event.
Across both days, participants could choose between three parallel breakout tracks: Convergence of IAM and GRC, led by Dr. Ludwig Fuchs; Tech Deep Dive: NEXIS Platform, led by Dr. Matthias Hummer; and the partner-focused NEXIS Platform Enablement track with Dr. Michael Kunz.
The smaller format created more room to dig into questions that are difficult to cover in a presentation, compare experiences and discuss specific challenges directly with peers and Nexis experts.
Sometimes the most useful answer is not another slide, but hearing how someone sitting across the table approached the same problem.
Celebrating the people behind the NEXIS Platform
This year’s INVOLVE also included a first: the NEXIS Awards.
Six awards recognized customers, partners and individuals whose contributions have helped shape both the NEXIS Platform and the community around it.
Helvetia received the Nexis Customer of the Year Award, while Munich Re was named Nexis Project of the Year. The Customer Lifetime Achievement Award went to Holger Hanke, and Timo Copp was recognized as Nexis Ambassador of the Year. iC Consult received the Nexis Partner of the Year Award, while Elisa Astfäller was named Nexis Seller of the Year.
Different awards, different contributions, but all six reflect something we value deeply at Nexis: the NEXIS Platform does not evolve in isolation. It grows through the people who use it, question it, implement it and share their experience with the wider community.
Because INVOLVE is about more than the agenda
INVOLVE is also about the conversations between the sessions.
Over coffee, at the Regensburger Dult and during the Weißwurst breakfast, there was plenty of time to exchange ideas, compare experiences and connect with others facing similar challenges.
These moments are an essential part of INVOLVE – bringing the community together beyond the stage.
Thank you
Two days pass quickly. What remains are new ideas, new connections and, hopefully, a few questions worth taking back into everyday work.
Thank you to all our customers, speakers, panelists and guests who shared their experiences so openly. And thank you to our partners for contributing their expertise and continuing to build with us.
A special thank you also goes to our sponsors. KOGIT and SonicBee supported INVOLVE as Platinum Sponsors, alongside our Gold Sponsors amiconsult, arcon, Axalon, cidaas, iC Consult, IDVKM, IPG, IS4IT, KPMG, One Identity, SailPoint and Ventum.
And, of course, thank you to Sebastian Rohr, who guided us through the event as our moderator, connected the many different perspectives on stage and kept the conversations moving throughout the two days.
Most of all, thank you to everyone who joined us in Regensburg and made INVOLVE what it is.
Because in the end, its value does not come from filling an agenda. It comes from bringing together people who are willing to share what they have learned, talk openly about what remains difficult and shape what comes next – together.
See you at the next NEXIS INVOLVE.